
Last updated October 14, 2026. Product claims, pricing shapes, and deployment options were checked against each vendor’s primary pages and docs on that date.
MCP gateways sit between AI clients and Model Context Protocol servers so enterprises can authenticate once, authorize tool calls, and keep an audit trail without handing every agent a raw credential. Without a gateway, each laptop and each IDE repeats OAuth, scatters secrets, and leaves security blind to shadow MCP.
This guide ranks ten gateways on identity depth, client admission, tool level policy, shadow MCP reach, audit export, and how heavy the ops burden is for platform and security teams. Placement is unpaid, per our editorial standards and disclosure policy.
It opens the MCP category under MCP and Agent Protocols, next to the AgentOps tools map, our observability tools roundup, and AI agent frameworks comparison. Pair it with tracing and eval cost work in LangSmith vs Langfuse vs Braintrust pricing when tool spend and observability spend land in the same budget review.
TL;DR
- Best directory resolved identity: Speakeasy (SSO plus SCIM, CIMD client admission, hooks beyond the gateway).
- Best security led shortlist: Runlayer (ToolGuard and AgentGuard, MDM based shadow AI, SOC 2 Type II).
- Best managed path with a store: Mintive, formerly MintMCP (hosted connectors, Teams from about $1,250/mo for 50 seats).
- Best air gap and marketplace story: Willow by Webrix (SaaS, self host, or on prem).
- Best if Kong already fronts APIs: Kong AI Gateway MCP plugins on Gateway 3.12+ Enterprise.
- Best AWS Bedrock native path: Amazon Bedrock AgentCore Gateway (OAuth or IAM inbound, credential vaulting outbound).
- Best model plus MCP on one pipe: TrueFoundry (Pro $25/user/mo; Enterprise adds VPC and air gap).
- Best self host OSS proxy with MCP: LiteLLM MCP gateway (virtual key scopes; Enterprise adds SSO and audit).
- Best Docker native POC: Docker MCP Gateway (Desktop Toolkit or open source CLI plugin).
- Best AKS session aware router: Microsoft MCP Gateway (open source Kubernetes control plane).
The 10 Best MCP Gateways at a Glance
Pick by the control job you need rather than by connector count marketing. Security wants identity and audit. Platform wants connectors and low ops. The table is the decision surface, and each section below explains when that gateway is rational for production agent traffic.
| Gateway | Best for | Principal on tool calls | Reach beyond gateway | Entry price shape |
|---|---|---|---|---|
| Speakeasy | Directory identity + agent hooks | IdP user via SSO/SCIM | Agent hooks + device agent | Deploy free path; Enterprise custom |
| Runlayer | Security owned MCP rollout | SSO user; Runlayer agent accounts | MDM shadow AI (Jamf/Intune/Kandji) | Custom enterprise quote |
| Mintive (MintMCP) | Managed store + hosted connectors | SSO user; Mintive agent IDs | Agent Monitor on laptops | Teams ~$1,250/mo (50 seats); Enterprise custom |
| Willow (Webrix) | Self serve catalog + air gap | Willow user record via upstream SSO | Endpoint sensors + Chrome extension | Free start; Enterprise custom |
| Kong AI Gateway | Kong shops governing MCP + APIs | Kong Consumer | Gateway traffic only | AI Gateway Enterprise meters |
| AWS AgentCore Gateway | Bedrock agents and AWS tools | JWT from OIDC or Cognito | Inside the AWS account | Managed AWS service pricing |
| TrueFoundry | Model routing + MCP governance | Gateway user with RBAC/ABAC | Gateway traffic only | Dev $0; Pro $25/user/mo |
| LiteLLM | One OSS proxy for models and tools | LiteLLM virtual key | Gateway traffic only | $0 OSS; Enterprise by capacity |
| Docker MCP Gateway | Container isolated POC | Per server env credentials | None built in | $0 open source / Desktop |
| Microsoft MCP Gateway | AKS session aware MCP routing | Bearer token + gateway RBAC | None | $0 open source |
How We Chose These Ten Gateways
We scored gateways on the two jobs enterprises actually buy: getting tools to agents, and governing what those agents do afterward. Prices and packaging change quickly, so every figure below is labeled as a list claim from a primary page, not a negotiated quote.
- Primary sources only: claims come from vendor product, pricing, and docs pages fetched October 14, 2026, including Speakeasy, Runlayer, Mintive, Kong, and AgentCore Gateway docs.
- Identity: whether each tool call resolves to a directory principal, a gateway local key, or a vendor minted agent account.
- Reach: whether the product sees MCP traffic that never hits the sanctioned gateway (hooks, MDM, device agents).
- Ops burden: fully managed SaaS versus single tenant AWS versus self host Kubernetes or Docker Desktop.
- Out of scope: pure LLM token routers without an MCP path (see our upcoming LLM gateway deep dives under AI Gateways), and observability suites covered in observability tools.
1. Speakeasy: Directory Identity With Reach Past the Gateway
Speakeasy ships its MCP gateway as part of an AI Control Plane aimed at both enablement and governance. People sync from Okta or Entra through SCIM, sign in through the corporate IdP, and each tool call can resolve to that directory user rather than a disposable key.
On the enablement side it acts as the OAuth client to upstream SaaS tools, holds per user tokens, converts internal APIs into generated MCP servers, and distributes bundles into coding agent marketplaces. On governance it supports Client ID Metadata Documents alongside Dynamic Client Registration, per server admission policy, tool and annotation scoped grants, and agent hooks plus a device agent for shadow MCP, per Speakeasy MCP gateway and enterprise gateway roundup.
Choose Speakeasy when offboarding must revoke tool access from the directory, and when you need visibility into agents that never open the sanctioned gateway URL. It does not replace a model router, so keep LiteLLM, Bifrost, or TrueFoundry on the inference path if you need provider failover.
2. Runlayer: Security First MCP Control Plane
Runlayer is the shortlist pick when the CISO owns the evaluation and wants runtime scanning on tool definitions, outputs, and whole sessions. Every MCP request passes a single tenant AWS gateway that authenticates, authorizes, scans, and logs before tools run.
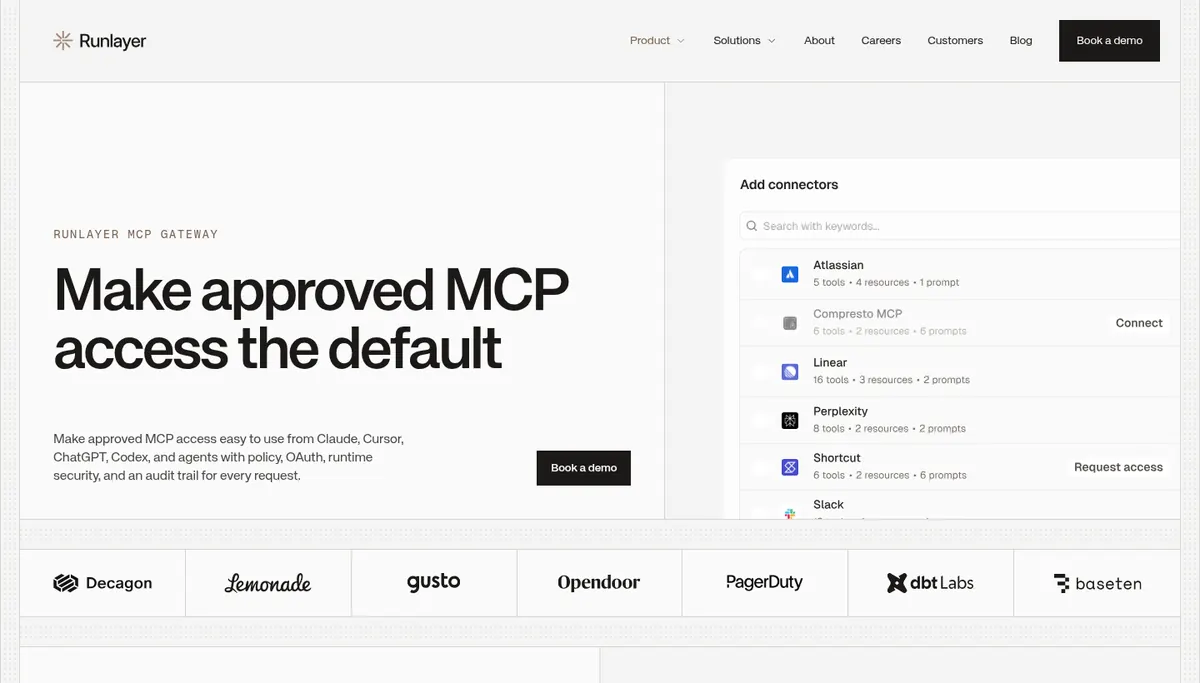
ToolGuard and AgentGuard map findings toward MITRE ATLAS style categories, while Watch reaches unmanaged laptops through MDM tools such as Jamf, Intune, and Kandji. The catalog and plugin path cover Claude, Cursor, ChatGPT, Codex, and hundreds of other clients, per Runlayer MCP Gateway.
Runlayer prices are custom enterprise quotes with no public list tier on the marketing site. Agent identities are Runlayer native accounts rather than Entra or Okta principals, which matters for offboarding design. Compliance claims on vendor materials include SOC 2 Type II, HIPAA, and GDPR.
3. Mintive (Formerly MintMCP): Managed Gateway and Store
Mintive, still reachable on mintmcp.com after the MintMCP rebrand, is the managed path for teams that want hosted connectors, a self serve MCP store, and role based bundles without standing up new infrastructure. The homepage positions one gateway that governs models, MCP tools, and context by role.
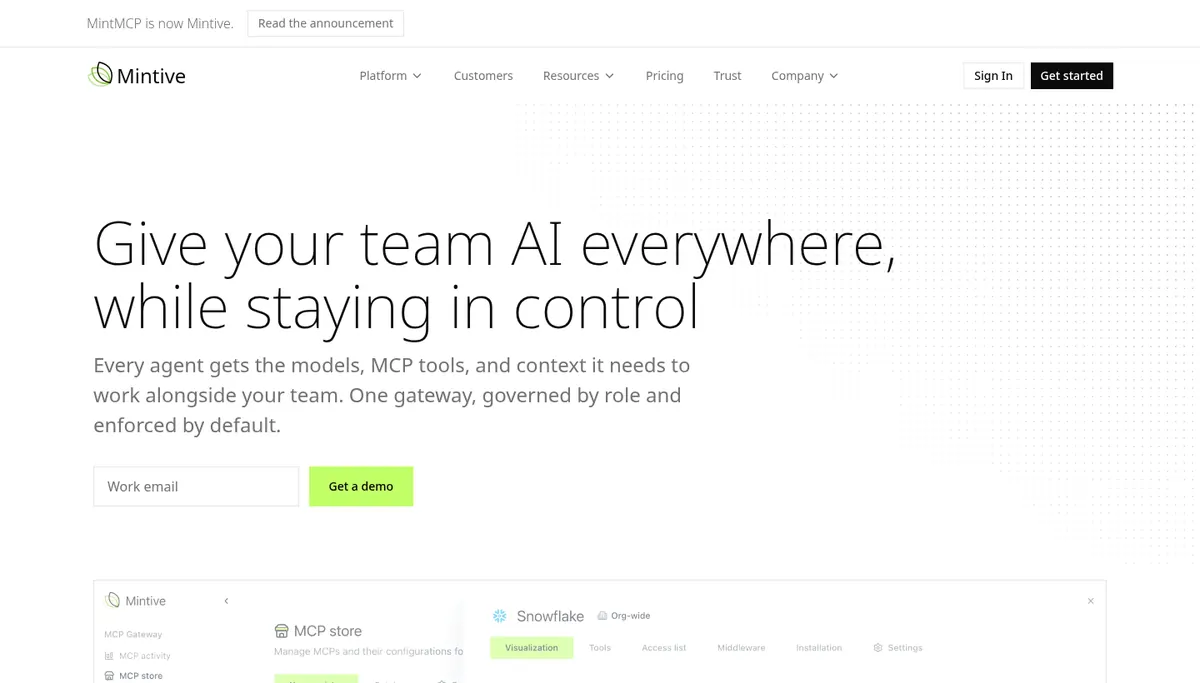
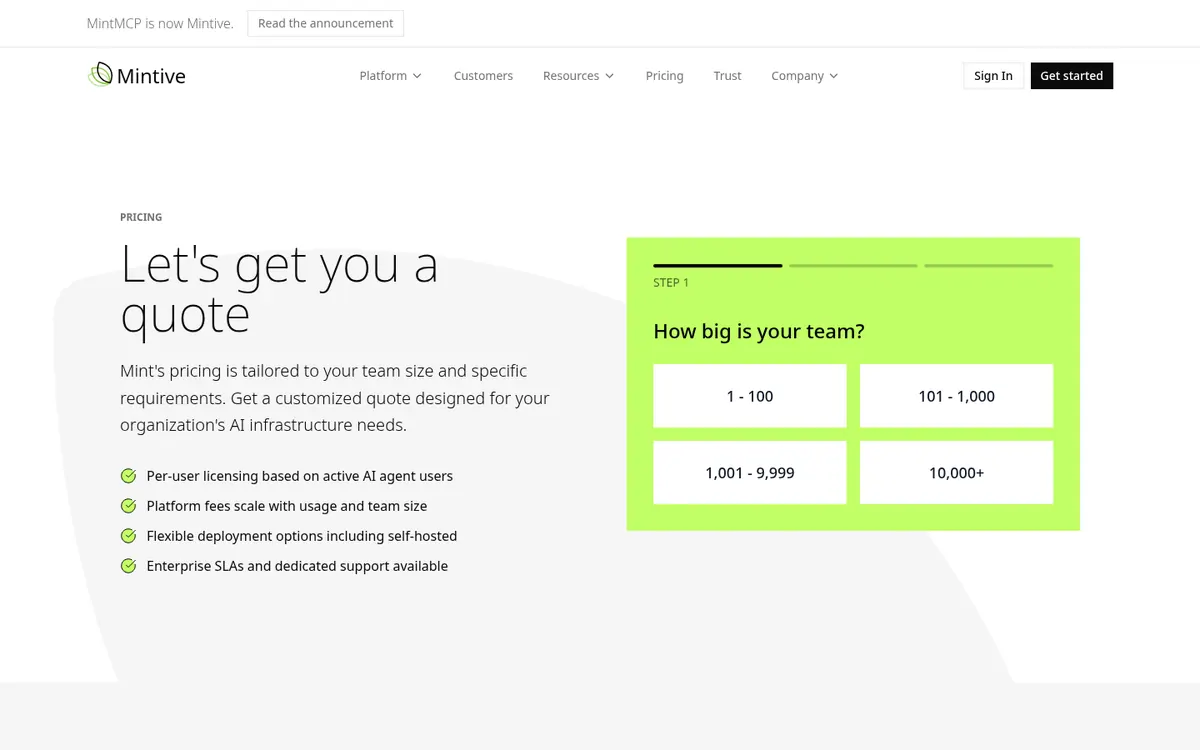
Public packaging describes per user licensing with platform fees, Teams around $1,250 per month for 50 included seats and $25 per extra seat in published commentary, and Enterprise custom for larger or regulated rollouts, per Mintive pricing. Trust materials list SOC 2 Type II, HIPAA aligned options, and cloud or self hosted deployment.
Pick Mintive when operations wants a store employees can browse after SSO, and when Agent Monitor on laptops is enough shadow coverage. Confirm whether agent identities stay Mintive native or also exist in your directory before you sign.
4. Willow by Webrix: Self Serve Enablement With Air Gap Options
Willow, the product marketed from webrix.ai after the Webrix rebrand path, wraps a governance gateway in a self serve enablement layer. Employees connect Claude, ChatGPT, Cursor, or automation clients to one secure entry point while admins keep SSO, group permissions, and audit logs.
Documented strengths include a large connector catalog, API to MCP conversion, endpoint sensors, a Chrome extension policy layer, and deployment as SaaS, self hosted cloud, or on prem air gap. Guardrails can mask or block secrets, PII, and prompt injection patterns on tool traffic, per Willow / Webrix.
Willow is the dedicated governance option when air gapped deployment is non negotiable and a marketplace matters as much as the proxy. Identity on each call follows Willow user records matched through upstream SSO and SCIM, so validate how that maps to your SIEM user keys.
5. Kong AI Gateway: MCP Plugins on the API Plane You Already Run
Kong extends API management into MCP through AI Gateway Enterprise plugins on Gateway 3.12 or later. AI MCP Proxy can passthrough MCP or convert OpenAPI routes into tools, while AI MCP OAuth2 validates access tokens and standard Kong plugins handle rate limits, logging, and ACLs.
Per tool ACLs on Consumers and Consumer Groups landed in 3.13 with allow and deny audit events. For enterprises that already operate Kong well, that is a working MCP gateway without a new vendor, per Kong AI Gateway and developer docs.
Kong is rational when MCP is a few internal APIs already behind Konnect, and a weak fit when you need directory principals or laptop shadow inventory. Consumer based identity and gateway only reach are the hard limits.
6. AWS AgentCore Gateway: Managed MCP on Bedrock
Amazon Bedrock AgentCore Gateway is the managed entry point for agents that already live on AWS. It converts OpenAPI, Smithy, and Lambda targets into MCP tools, fronts other agents, and handles inbound JWT or IAM auth plus outbound credential injection in one service.
Recent extensions cover richer tool schemas, prompts and resources as first class primitives, streaming sessions, elicitation, OAuth on behalf of flows, interceptors, and Cedar based AgentCore Policy checks logged into CloudWatch, per AgentCore and Gateway docs.
Start here when tools are AWS hosted APIs and Lambda functions and your agents already run on Bedrock. Traffic that never enters the account, including a laptop pointed at a third party MCP server, stays outside its inventory.
7. TrueFoundry: Model Routing With MCP Governance Attached
TrueFoundry began as an AI gateway for routing across many model providers and extended the same control plane to MCP tool traffic. Platform teams that already need failover, semantic caching, and spend controls can keep MCP governance on the same pipe.
Pro list pricing is $25 per user per month on published pages, with Developer free and Enterprise adding VPC, on prem, and air gap paths. RBAC, ABAC, and Cedar or OPA style policies sit beside orchestrated guardrail providers, per TrueFoundry AI gateway and pricing.
TrueFoundry wins when model routing is the primary buy and MCP is the second workload on the same gateway. It does not invent device reach, so unsanctioned laptop MCP remains a separate program.
8. LiteLLM: Open Source Proxy That Also Speaks MCP
LiteLLM is the incumbent open source LLM proxy, and its MCP gateway extends the same virtual keys, teams, and budgets to tool servers registered in the UI or config.yaml. Teams that already self host LiteLLM for model traffic can add MCP without a second control plane.
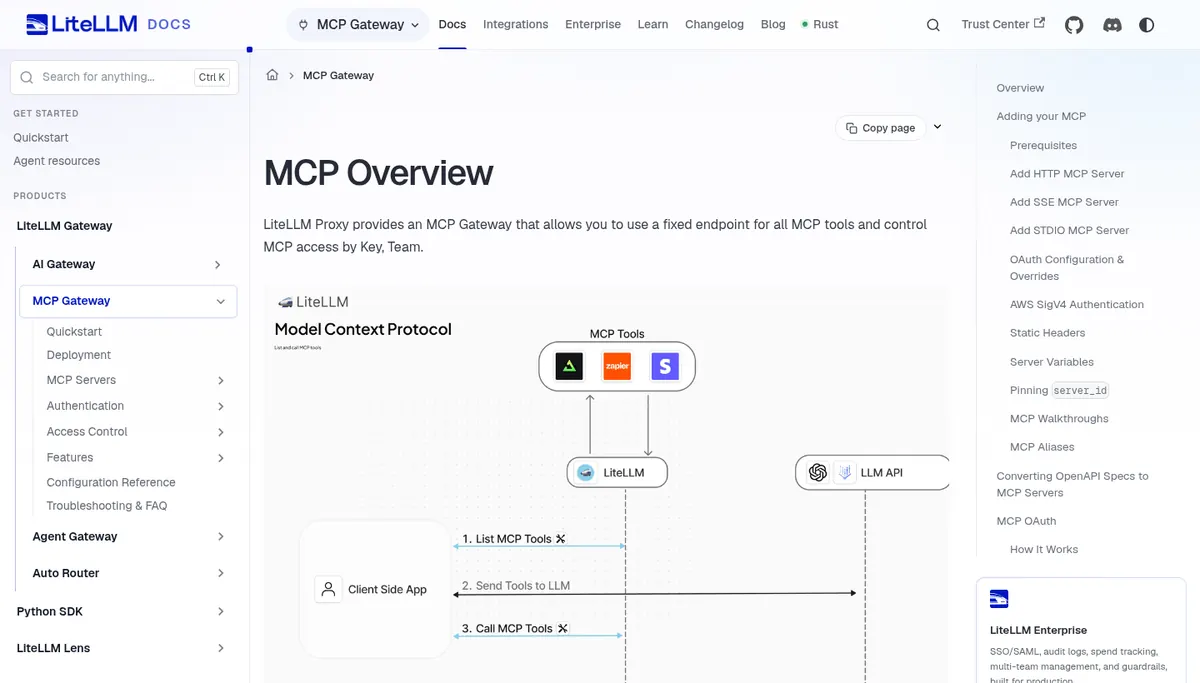
Access can be scoped by key, team, and organization, with OAuth to upstream MCP servers and spend tracked per server. Enterprise packaging adds SSO, SCIM, and audit logs on top of the MIT core, per LiteLLM MCP docs.
LiteLLM is the right self host default when you accept key based identity and will map directory users onto virtual keys yourself. There is no endpoint agent, so shadow MCP detection is your problem.
9. Docker MCP Gateway: Container Isolation for a Scoped POC
Docker MCP Gateway orchestrates MCP servers as isolated containers with restricted privileges, injected credentials, and centralized routing for clients that point at the gateway instead of each server. On Docker Desktop with MCP Toolkit active, the gateway can run in the background without a separate install.
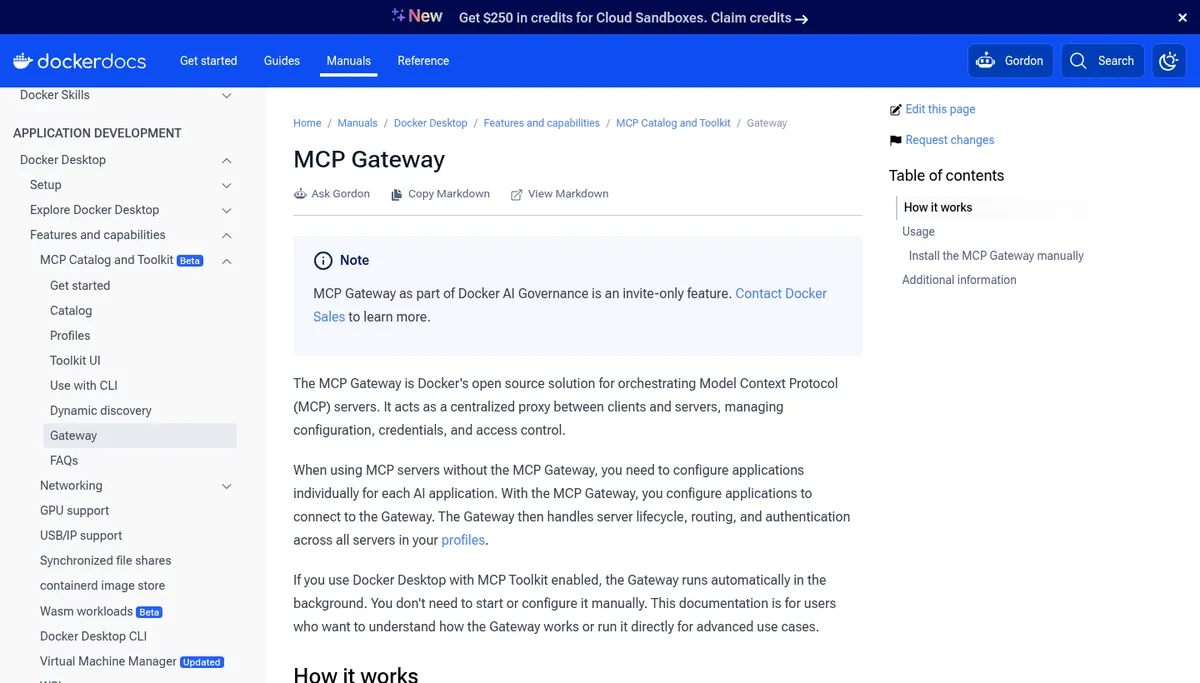
Docs describe profile based server sets, lifecycle management, and an open source CLI plugin path for Docker Engine hosts. Enterprise AI Governance packaging for the gateway is invite only through Docker Sales, per Docker MCP Gateway docs.
Use Docker when a single team is validating one or two servers before a governed rollout, not as the long term RBAC and SIEM answer. Build authz and structured audit in front, or plan the migration path to a governance gateway early.
10. Microsoft MCP Gateway: Session Aware Routing on Kubernetes
Microsoft MCP Gateway is an open source reverse proxy and control plane for running many MCP servers on Kubernetes, including Azure Kubernetes Service. It keeps session affinity so a session ID lands on the same server instance, and it exposes deploy, update, and delete workflows for operators.
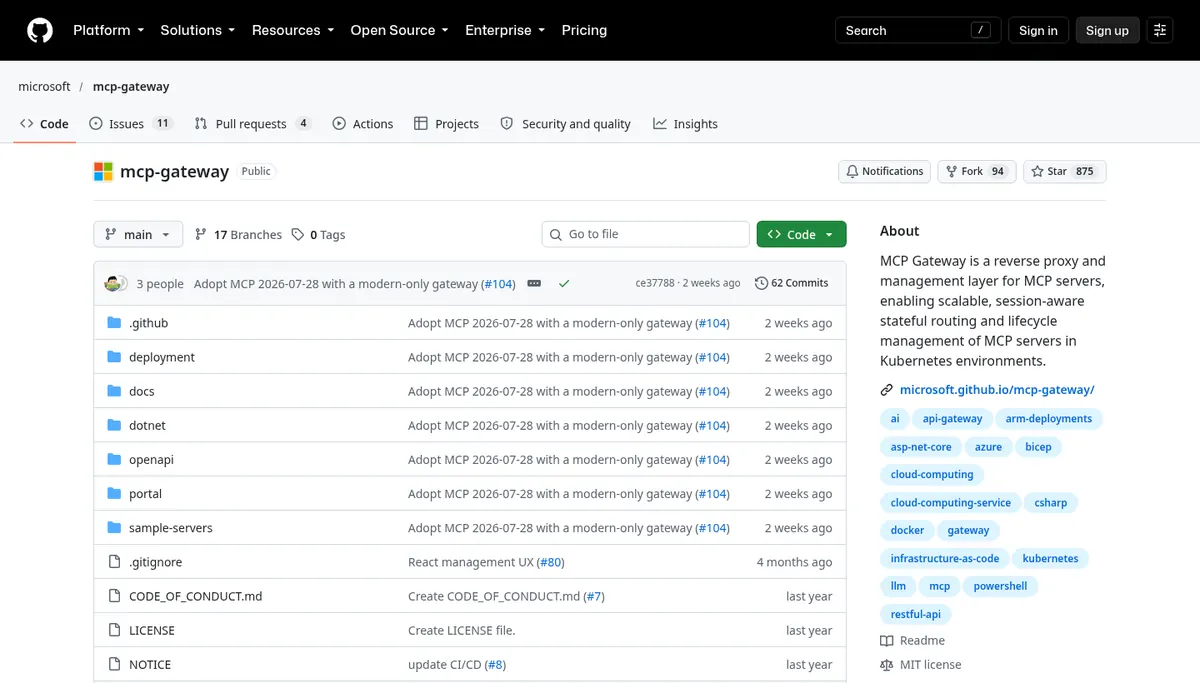
Authentication is bearer token based with RBAC on data and control planes. It is infrastructure in the strict sense: it makes multi server MCP on AKS tractable and leaves directory mapping, tool level policy, and threat detection to layers around it, per microsoft/mcp-gateway.
Choose Microsoft MCP Gateway when AKS operations are already a strength and you will bring a separate identity and policy product. Treat it as a POC plus production router, then add a separate governance plane for directory policy and threat detection.
Decision Table: Identity Versus Reach
Most evaluations collapse into two questions that decide the shortlist before demos start. First, who is named on each tool call in the audit log. Second, whether the product sees traffic that skips the sanctioned gateway. Use this matrix to cut vendors that cannot answer either question cleanly.
| If your constraint is… | Start with | Verify next |
|---|---|---|
| Directory principal on every call + shadow MCP | Speakeasy | CIMD admission policy and device agent coverage |
| Security owned scanning and MDM inventory | Runlayer | Agent account offboarding and quote fit |
| Managed store with minimal ops | Mintive | Seat math at 50+ users and agent ID model |
| Air gap or on prem mandatory | Willow, TrueFoundry, or LiteLLM | Which controls stay in the air gapped build |
| Already on Kong or Bedrock | Kong or AgentCore Gateway | When directory identity becomes a hard requirement |
| One self host proxy for models and tools | LiteLLM (or Bifrost if latency claims dominate) | How you map IdP users onto keys |
| Scoped POC this quarter | Docker or Microsoft MCP Gateway | Exit criteria into a governance gateway |
What Security and Platform Teams Usually Miss
Search results often treat any MCP proxy as an enterprise gateway, which collapses enablement and governance into one checkbox. The gaps below are where rollouts fail after a green POC, usually in the first security review or the first offboarding ticket that nobody can close from the directory alone.
- Offboarding lag: revoking a person in Okta must deny the next tool call without a manual gateway edit.
- Open DCR: Dynamic Client Registration alone lets unverified clients mint identities you cannot allowlist cleanly.
- Annotation versus deny: hiding a write tool in a catalog is not the same as refusing the call at runtime.
- Laptop blind spots: a gateway that only sees sanctioned traffic will miss Cursor pointed at a personal MCP server.
- Budget coupling: tool call spend and tracing spend show up together; keep observability pricing in the same review packet.
Primary, Secondary, and Long-Tail Questions This Guide Answers
- Primary: What are the best MCP gateways for enterprise security and scale in 2026?
- Secondary: Kong versus AWS AgentCore versus Docker for MCP; Mintive versus Runlayer versus Speakeasy for governance.
- Long tail: Which MCP gateway supports CIMD, MDM shadow detection, air gap, or AKS session affinity?
- Related stack: pair tool governance with evaluation tools, Langfuse vs LangSmith vs Braintrust, and Langfuse alternatives when agents move from laptop demos into production.
Frequently Asked Questions
What is an MCP gateway in enterprise terms?
An MCP gateway sits between AI clients and Model Context Protocol servers. It centralizes authentication, authorizes which tools a role may call, injects upstream credentials, and writes an audit trail. Enterprises buy it to stop every laptop from holding raw secrets and to make offboarding and SIEM export tractable.
Is Kong or AWS AgentCore enough without a governance vendor?
Yes for a narrow case: a few internal APIs already behind Kong, or Bedrock agents calling AWS hosted tools through AgentCore Gateway. Add a governance product when directory resolved identity, client admission policy, or inventory of unsanctioned laptop MCP becomes a hard requirement from security.
How should we price an MCP gateway proof of concept?
Model seats or request capacity for the sanctioned path, then add engineering time for identity mapping and SIEM export. Managed options quote per user; OSS options trade license fees for SRE time. Force the POC to test offboarding, deny rules, and shadow traffic rather than stopping at happy path tool calls.
What is the difference between CIMD and DCR for MCP clients?
Dynamic Client Registration lets any client post a name and redirect URI to mint a client id with little verification. Client ID Metadata Documents point at a vendor hosted URL an allowlist can name. Enterprise gateways should support both while coding agents finish CIMD adoption across the ecosystem.
Which MCP gateway is best for air gapped deployment?
Willow documents on prem and air gap paths among dedicated governance products. TrueFoundry and LiteLLM also self host, including air gapped Kubernetes patterns. Speakeasy is primarily a hosted control plane with optional self hosted data plane, so confirm residency needs before shortlisting.
Related Guides
Narrowing the shortlist to the three platform defaults? Our head-to-head Kong vs AWS AgentCore vs Docker compares MCP gateway auth, hosting model, and pricing for teams already committed to one of those stacks.
Before you shortlist gateways, get the protocol basics straight. Our MCP Explained guide covers servers, gateways, and security patterns enterprises actually ship.
- MCP category hub and MCP and Agent Protocols
- AgentOps tools map and AI Gateways
- 12 Best AI Agent Observability Tools and open source LLM observability
- LangSmith vs Langfuse vs Braintrust pricing and Langfuse vs LangSmith vs Braintrust
- 12 Best AI Agent Frameworks and AI agent evaluation tools
- Editorial standards, disclosure, contact