
Last updated October 21, 2026. Ownership, pricing, documentation access, and product details were checked against each vendor’s public pages and announcements on that date.
The best non-human identity tools for securing AI agents in 2026 are Okta for AI Agents and Microsoft Entra Agent ID for teams on those identity providers, and Aembit for runtime access without stored secrets. Token Security, Oasis Security, SailPoint Entro, Idira Secure AI Agents, and Clutch Security complete the list of eight.
Start with the identity provider you already run, because it can register agents, issue short-lived tokens, and pull them into the same access reviews as employees. Add a specialist when you need to find agents nobody registered or broker credentials at runtime. Skip the specialists if your agents all run inside one vendor’s platform and you already govern that platform well.
A non-human identity (NHI) is any credential that software uses to act, such as an API key, OAuth token, service account, or AI agent identity. NHI tools find those identities, assign each an owner, cut their access, and watch how they are used. This guide sits in our agent security coverage within AI governance and security. No vendor paid for placement or reviewed this page, per our editorial standards and disclosure policy. Our report on a contractor Claude Code agent on a Pentagon network shows what happens when an agent holds unmanaged credentials.
TL;DR
- The category consolidated fast in 2026. Palo Alto Networks closed CyberArk on February 11, Cisco closed Astrix and SailPoint closed Entro on June 29, and Cyera closed its $1 billion Oasis deal on September 3.
- Astrix is no longer sold on its own. Its site says standalone sales of new licenses ended on June 30, 2026, so new buyers get Astrix through Cisco.
- Only 2 of 9 vendors we checked publish a list price. Aembit charges $20 per agent a month after a free tier of 3 agents, and Microsoft charges $15 per user a month for Agent 365.
- 4 of 9 vendors keep product docs behind a login. Token Security, Oasis, SailPoint Entro, and Clutch Security all redirected our documentation checks to sign-in pages.
- Identity providers now cover agents directly. Okta made Agent SSO part of core Okta SSO at no extra cost on August 24, and Entra Agent ID is available to every Microsoft Entra customer.
8 Best Non-Human Identity Tools at a Glance
Choose an NHI tool by where your agents live first, then by whether you need discovery, runtime credential brokering, or access governance. The table compares all eight on fit, control layer, ownership, and published price, based on vendor pages and announcements checked on October 21, 2026.
| Tool | Best for | Main control layer | Owner (October 2026) | Published price |
|---|---|---|---|---|
| Okta for AI Agents | Enterprises already on Okta | Directory, tokens, and reviews | Okta | Separate subscription, unpriced |
| Microsoft Entra Agent ID | Microsoft 365 and Azure shops | Directory and Conditional Access | Microsoft | Agent 365 at $15 per user a month |
| Aembit | Runtime access without stored secrets | Credential broker and MCP gateway | Independent | Free for 3 agents; $20 per agent a month |
| Token Security | Independent discovery with intent-based limits | Discovery and posture | Independent | Quote only |
| Oasis Security | Agent access across cloud and SaaS | Access management and lifecycle | Cyera | Quote only |
| SailPoint Entro | SailPoint customers and secrets lineage | Discovery, secrets, and detection | SailPoint | Quote only |
| Idira Secure AI Agents | CyberArk privileged access customers | Identity broker for MCP | Palo Alto Networks | Add-on license, unpriced |
| Clutch Security | Independent NHI, secrets, and agent coverage | Discovery and lineage | Independent | Quote only |
Verdict: Choose your identity provider’s agent product when most agents connect to apps that identity provider already protects. Choose Aembit or Idira when agents call MCP servers and APIs and you want a broker in the path. Choose Token Security, Oasis, Entro, or Clutch when the first job is finding agents and keys that nobody registered.
How We Ranked These Non-Human Identity Tools
We ranked tools on how much of the agent identity job each one covers and how much a buyer can verify before signing. We started from vendors that ship AI agent identity features as of October 21, 2026, then read each vendor’s product pages, documentation, pricing, and 2026 announcements.
- Discovery: whether the tool finds agents and the keys they use, including agents nobody registered.
- Credential model: whether agents get short-lived, scoped credentials in place of standing secrets.
- Runtime control: whether the tool sits in the request path to MCP servers and APIs, or only reports on access.
- Governance: whether each agent gets a human owner, access reviews, and a way to shut it off.
- Buyability: ownership changes, standalone sales, public pricing, a free tier, and public documentation.
We did not deploy these tools in a production tenant, so there are no star ratings. For the protocol layer underneath, see MCP explained, and for tools that scan MCP servers themselves, see our MCP security tools guide.
What Our October 21 Buyer Access Check Found
Of 9 agent identity vendors we checked, only Aembit offered a public price, a free tier, and open documentation together, and 4 had changed owners during 2026. We visited each vendor’s product, pricing, and documentation pages on October 21, 2026 and recorded what a buyer could see without booking a call.
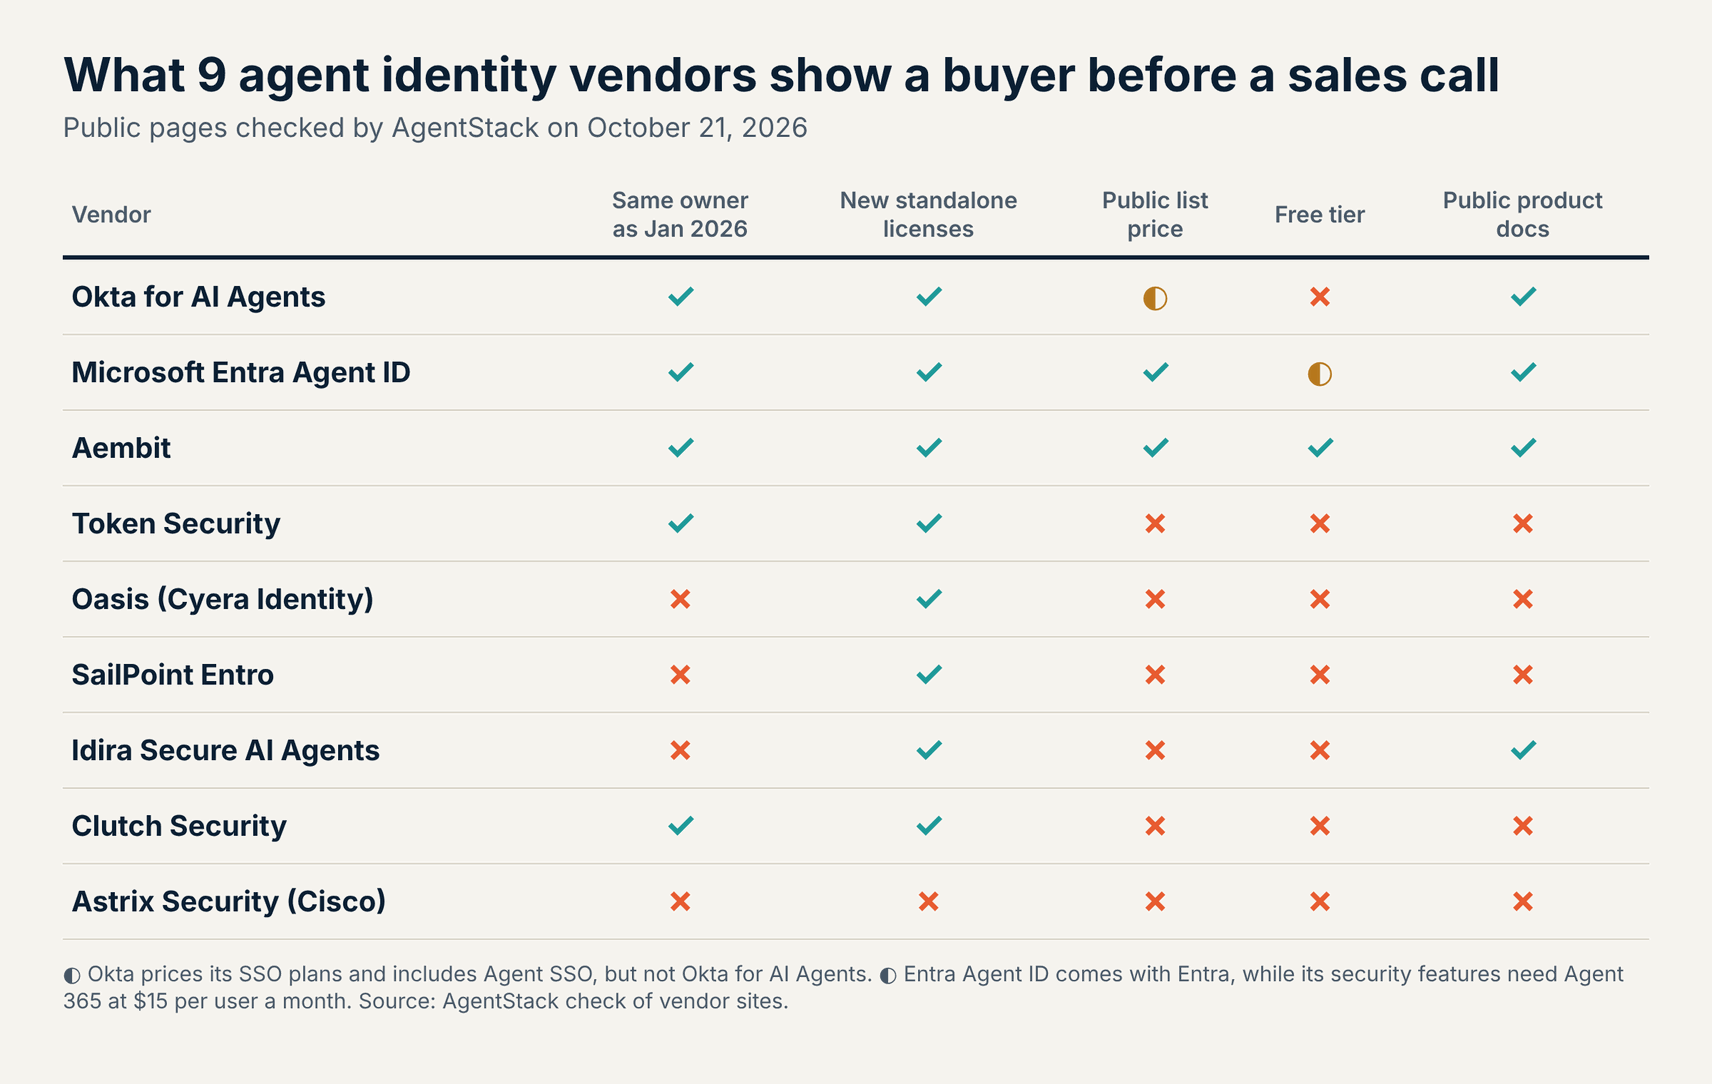
- Ownership moved at 4 of 9. Idira (CyberArk), Astrix, SailPoint Entro, and Oasis all sit under a new parent compared with January 2026.
- Astrix stopped selling new licenses. It is the only vendor of the nine with no standalone path for a new customer.
- Public prices are rare. Aembit lists $20 per agent a month, and Microsoft lists Agent 365 at $15 per user a month. Okta prices its SSO plans, which now include Agent SSO, but not Okta for AI Agents.
- Documentation is often gated. Requests to the docs sites for Token Security, Oasis, Entro, and Clutch redirected to login pages. Okta, Microsoft, Aembit, and Idira publish their agent docs openly.
- Only Aembit has a free tier. Microsoft includes Entra Agent ID with Entra, but its agent security features need an Agent 365 license.
Gated docs and quote-only pricing slow a proof of concept more than any missing feature does. Ask each shortlisted vendor for documentation access and a written price range before the first demo. Teams writing an incident plan for rogue agents can pair this with the NIST, NSA, and CISA response practices.
Six Agent Identity Deals That Closed in 2026
Six identity vendors bought or completed deals for agent and machine identity specialists between February and September 2026. The pattern matters for buyers, because a tool bought today may be renamed, bundled, or withdrawn within a year, as Astrix was after Cisco closed its acquisition on June 29.
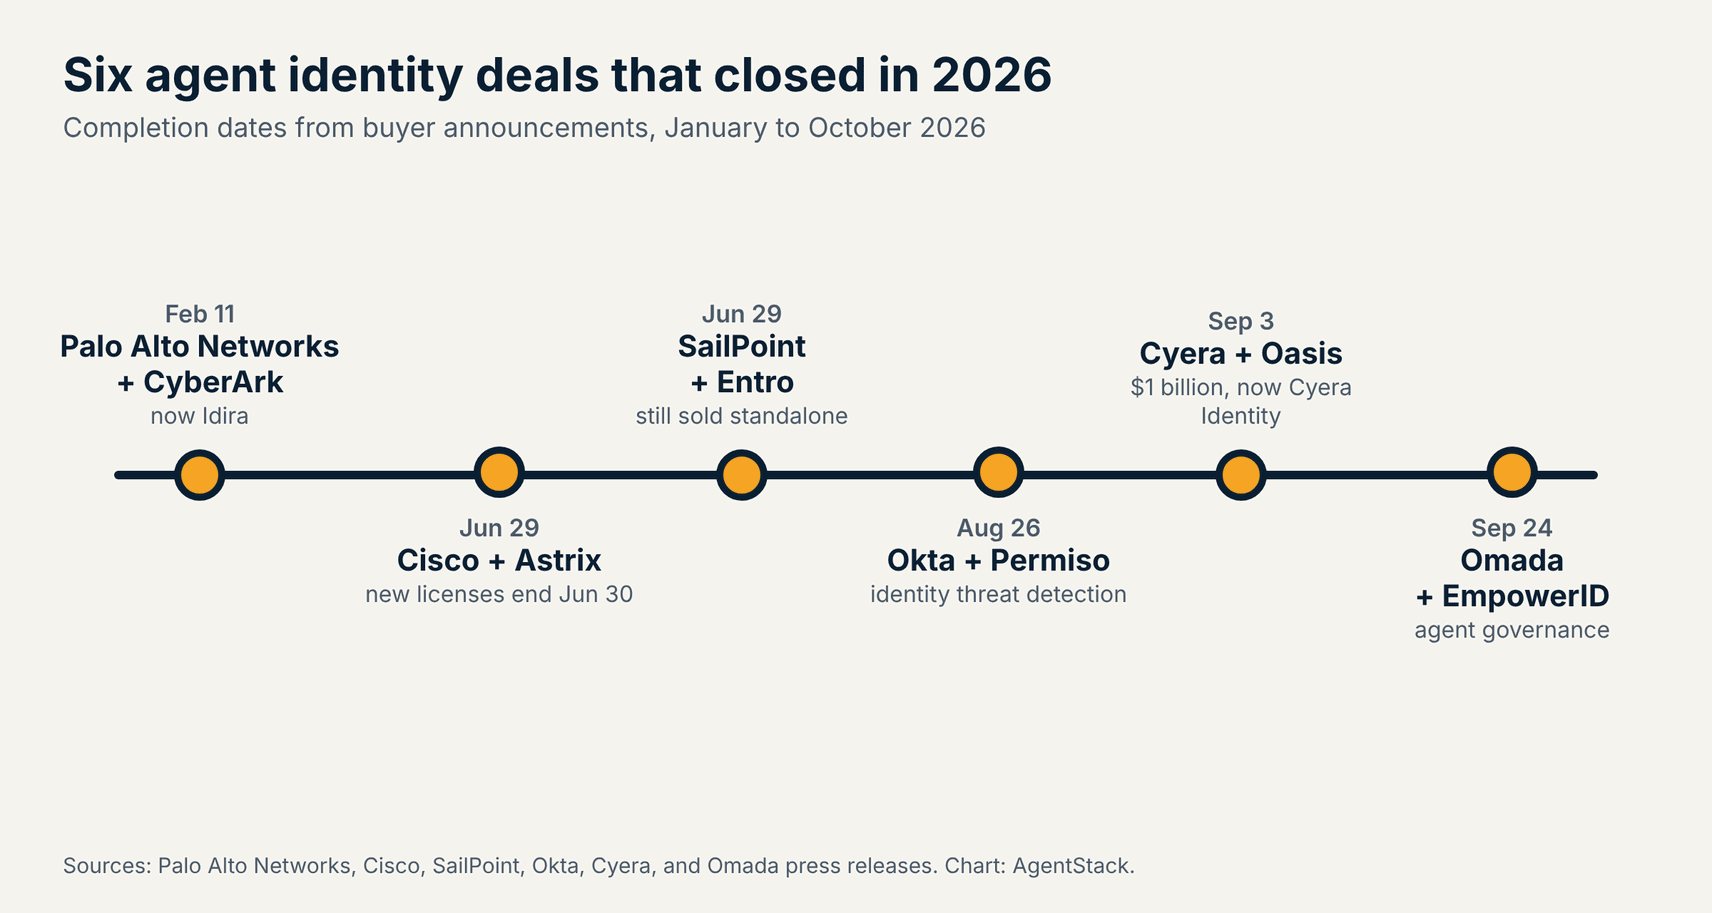
Cisco plans to fold Astrix into Cisco Identity Intelligence, Secure Access, and Duo. Okta closed its Permiso deal on August 26 to add identity threat detection, and Omada acquired EmpowerID on September 24 for runtime agent governance.
1. Okta for AI Agents: Best for Okta Workforce Customers
Okta for AI Agents is the strongest pick for companies already on Okta, because agents land in the same directory, access reviews, and audit logs as employees. Okta announced general availability on April 29, 2026, per its launch post. Agents get human owners, scoped short-lived tokens, and a deactivation switch that the security team can use as a kill switch.
Discovery runs through Okta Identity Security Posture Management, which finds browser OAuth grants, agents and MCP servers on endpoints through CrowdStrike Falcon, and agents built in Salesforce Agentforce and Microsoft Copilot Studio, per Okta’s discovery docs. Agent SSO, based on the open Cross App Access protocol, went GA on August 24, 2026, inside core Okta SSO at no extra cost, per Okta’s announcement.
- Best for: Okta Workforce Identity customers that want agents governed with the same lifecycle tools as staff.
- Pricing (October 2026): Agent SSO is included in core Okta SSO. Okta for AI Agents is a separate subscription with no public price.
- Watch out for: Agent SSO only covers agents and apps that support Cross App Access, and the posture management discovery features are excluded from the FedRAMP Core version.
2. Microsoft Entra Agent ID: Best for Microsoft 365 and Azure Shops
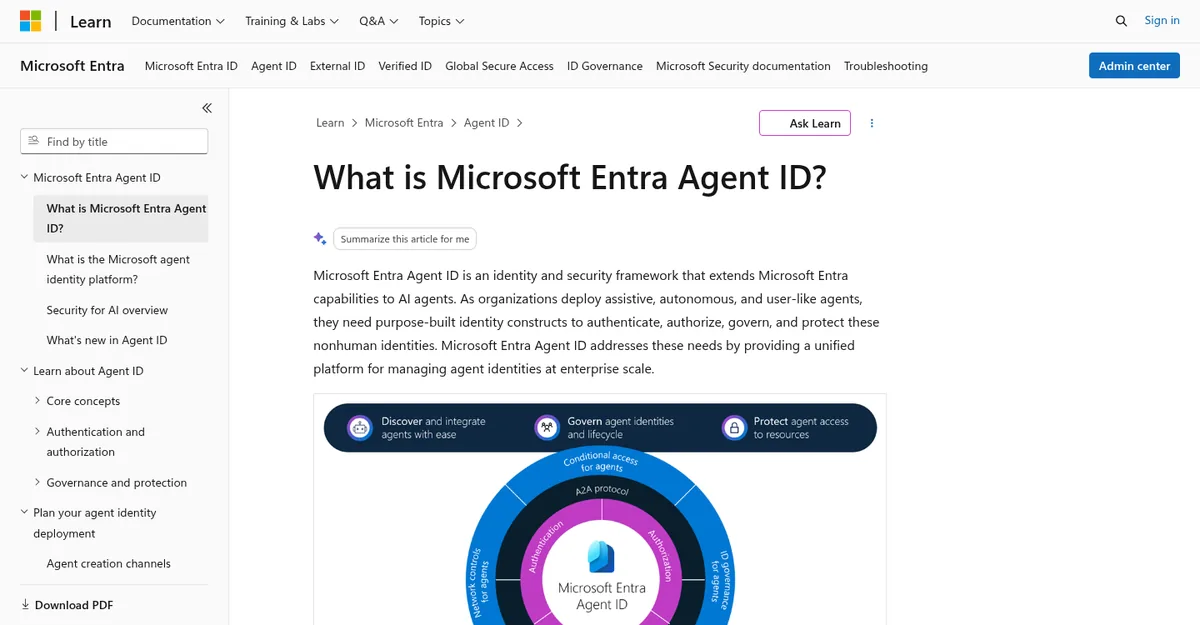
Microsoft Entra Agent ID is the natural choice for Microsoft 365 and Azure tenants, since agent identities live in Entra and inherit Conditional Access, ID Protection, and ID Governance. Microsoft lists it as generally available and says Agent ID is available to all Microsoft Entra customers, per its overview.
Agents are created from identity blueprints with named sponsors, and new Conditional Access templates block risky agent identities or set rules for autonomous agents, per Microsoft’s release notes. It also covers agents outside Microsoft through a sidecar or federation, with guides for Amazon Bedrock and n8n. Our report on Microsoft Dynamic Agent Risk and Guardian Agents covers the risk scoring layered on top.
- Best for: Organizations whose agents run in Copilot Studio, Azure AI Foundry, or Microsoft 365.
- Pricing (October 2026): Agent ID comes with Entra. Extending Entra security features to agents needs Agent 365 at $15 per user a month paid yearly, or Microsoft 365 E7 at $99 per user a month, per Microsoft’s pricing page.
- Watch out for: Conditional Access for agents acting on a user’s behalf follows that user’s license, so those users need Microsoft 365 E3, and ID Protection needs E5.
3. Aembit: Best for Runtime Access Without Stored Secrets
Aembit is the best fit for teams that want agents to hold no long-lived credentials, because it checks policy on every request and swaps in a short-lived, scoped credential. IAM for Agentic AI went GA in April 2026 with two parts, per Aembit’s launch post: a managed MCP Authorization Server that follows the OAuth 2.1 flow in the MCP specification, and an MCP Identity Gateway that runs as a Linux virtual machine in your network.
Its Blended Identity model evaluates the user and the agent together, so an engineer can reach Jira through Claude Desktop while only the security team can reach a scanner through the same client. The gateway shipped version 1.35.6086 on October 14, 2026, per Aembit’s release page.
- Best for: Platform and security teams that want to broker agent access to MCP servers, APIs, and SaaS with no stored secrets.
- Pricing (October 2026): Free for 3 AI agents, 1 MCP Identity Gateway, and 5 authorization policies. Teams is $20 per agent a month for 10 to 500 agents, and Enterprise is custom, per Aembit’s pricing page.
- Watch out for: Aembit governs the agents you route through it, so pair it with a discovery tool to find agents that connect around it.
4. Token Security: Best for Independent Discovery With Intent-Based Limits
Token Security suits enterprises that want an independent platform to find agents, assign owners, and trim each agent to the permissions its stated purpose needs. It launched intent-based AI agent security on March 18, 2026, which compares declared and observed intent with granted access and flags actions outside that boundary, per its announcement.
The platform maps AI agents, MCP servers, humans, secrets, and permissions in one identity graph, and it ships its own MCP server so analysts can query findings from Claude, ChatGPT, or Cursor, per Token’s homepage. Token raised a $20 million Series A in January 2025, per TechCrunch.
- Best for: Security and identity teams that want discovery, posture, and lifecycle for agents from a vendor outside the big identity suites.
- Pricing (October 2026): No public price; sold through demos and quotes.
- Watch out for: Product documentation sits behind a login, so ask for access before a proof of concept.
5. Oasis Security: Best for Agent Access Across Cloud and SaaS
Oasis Security fits enterprises that want time-bound, intent-aware access for agents across IaaS, SaaS, PaaS, and on-premises systems from one platform. Its Agentic Access Management product inventories agents and their identities, provisions access for only as long as a task needs it, and enforces policy across clouds, vaults, and SaaS apps, per its homepage.
Cyera completed its acquisition of Oasis on September 3, 2026, in a deal valued at $1 billion, and the platform will operate as Cyera Identity, per Cyera. Oasis says a Fortune 500 logistics customer cut secret rotation effort by 35%, a vendor-reported figure we could not verify independently.
- Best for: Large enterprises, especially Cyera data security customers, governing agent access across many clouds and SaaS apps.
- Pricing (October 2026): No public price; sold through demos and quotes.
- Watch out for: The product is moving to the Cyera Identity name, so confirm contract terms, roadmap, and support owner before you sign.
6. SailPoint Entro: Best for SailPoint Customers and Secrets Lineage
SailPoint Entro is the pick for SailPoint identity governance customers and for teams that need every secret traced to a human owner. SailPoint completed the Entro acquisition on June 29, 2026, and still sells Entro as a standalone product while it integrates with SailPoint Agentic Fabric, per SailPoint.
Entro discovers agents, MCP servers, and secrets across cloud, SaaS, code, and endpoints, and it adds just-in-time access through Agentic Access Administration, per SailPoint’s product page. It can also capture prompt sessions from Claude, Cursor, and Gemini and detect unusual behavior at the identity layer.
- Best for: SailPoint customers and AppSec teams that want NHI discovery tied to secret exposure.
- Pricing (October 2026): No public price; sold through SailPoint.
- Watch out for: Prompt session capture collects sensitive content, so run a privacy review before you switch it on.
7. Idira Secure AI Agents: Best for CyberArk Privileged Access Customers
Idira Secure AI Agents is the best route for CyberArk customers, because it applies zero standing privilege to agents through the same platform that already guards human admins. Palo Alto Networks completed its CyberArk acquisition on February 11, 2026, and launched the Idira platform on May 12, 2026, per its announcement.
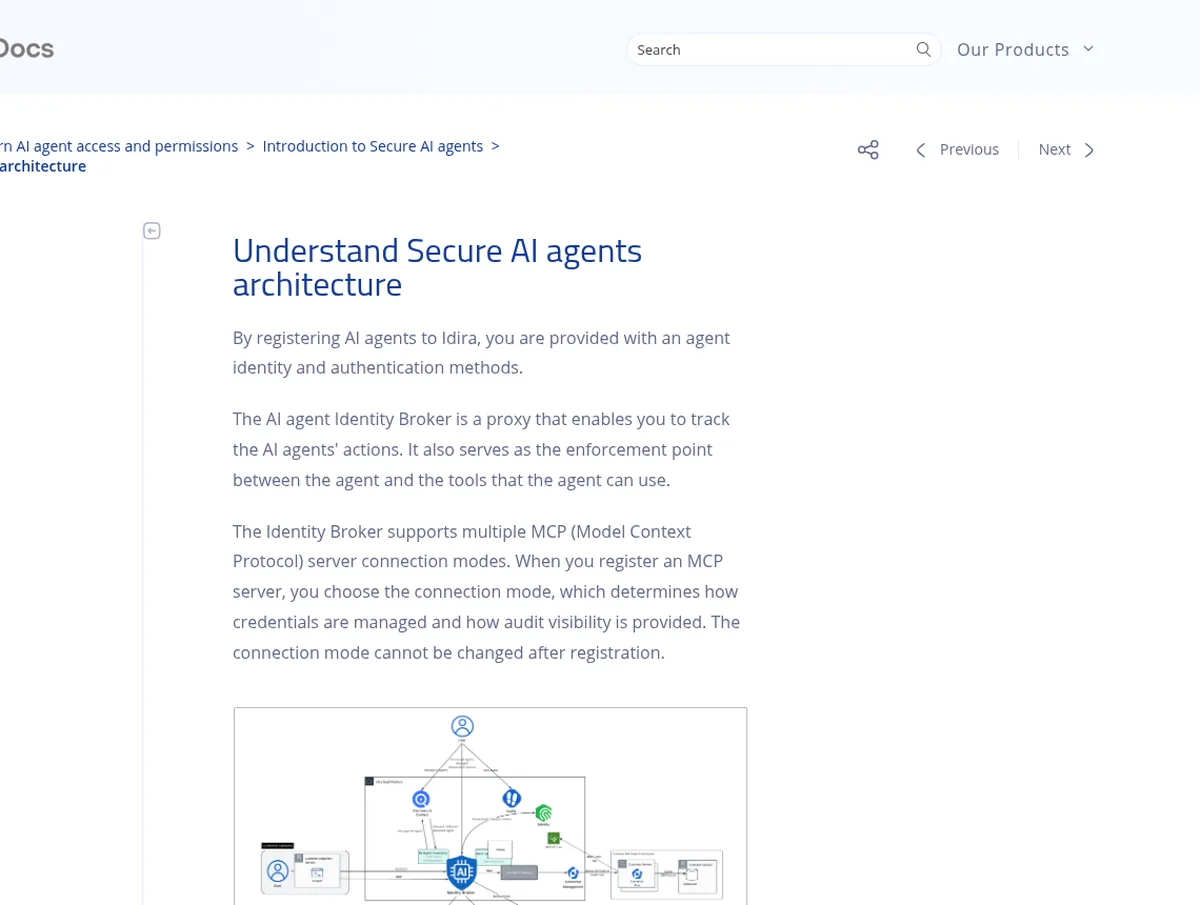
Agents reach MCP servers through an Identity Broker, a proxy that gives each server a URL in the form https://<tenant-gateway-host>/mcp/<serverName> and hides the real server address, per the architecture docs. Discovery covers AWS Bedrock, AWS AgentCore, and Microsoft Copilot Studio, per the introduction.
- Best for: CyberArk privileged access customers that want agent access brokered, audited, and granted per task.
- Pricing (October 2026): Agentic and machine identity protections are sold as additional licenses on Idira, with no public price.
- Watch out for: An MCP server’s connection mode cannot be changed after registration, so choose between broker-held OAuth and passthrough carefully.
8. Clutch Security: Best for Independent NHI, Secrets, and Agent Coverage
Clutch Security suits teams that want one independent platform covering service accounts, secrets, and AI agents, with each one traced back to the person who created it. Its Identity Lineage maps every agent to the credentials it uses, the resources they reach, and a human owner, per Clutch’s guardrails explainer.
Clutch issues short-lived, task-scoped credentials in place of keys an agent inherits from a developer’s shell, and it lists over 100 integrations, including AWS IAM, Entra ID, Okta, HashiCorp Vault, Bedrock, and Vertex AI. It repositioned around NHI, secrets, and agent security in a May 4, 2026 post and raised a $20 million Series A in January 2025, per TechCrunch.
- Best for: Cloud security teams that want NHI, secrets, and agent findings in one graph from an independent vendor.
- Pricing (October 2026): No public price; sold through demos and quotes.
- Watch out for: The homepage did not name MCP in our check and docs require a login, so confirm MCP server coverage in a demo.
How to Find the Credentials Your Agents Already Use
You can start an NHI inventory before buying anything by listing long-lived keys and third-party app grants in the systems agents touch most. The two commands below list active AWS access keys with their creation dates and the GitHub Apps installed in an organization.
# Active AWS IAM access keys and when each was created (AWS CLI v2)
for u in $(aws iam list-users --query 'Users[].UserName' --output text); do
  aws iam list-access-keys --user-name "$u" \
    --query 'AccessKeyMetadata[?Status==`Active`].[UserName,AccessKeyId,CreateDate]' \
    --output text
done

# GitHub Apps installed in an organization (GitHub CLI)
gh api /orgs/YOUR_ORG/installations \
  --jq '.installations[] | [.app_slug, .created_at] | @tsv'
Old keys with no clear owner are the first candidates for rotation, per the AWS list-access-keys reference and GitHub’s installations endpoint. Agents that call MCP servers also need a policy layer, which our MCP gateways guide and MintMCP vs Runlayer vs Lasso comparison cover.
Discovery, Runtime Access, and Governance Compared
NHI tools split into three jobs: finding agents and keys, issuing credentials at runtime, and governing access over time. Few tools do all three equally well, so the table shows where each of the eight is strongest, based on vendor documentation and product pages checked on October 21, 2026.
| Tool | Finds unregistered agents | Short-lived credentials | In the request path | Owners and reviews |
|---|---|---|---|---|
| Okta for AI Agents | Browser, endpoint, and builder platforms | Scoped tokens | Agent SSO; Agent Gateway announced | Certifications and deactivation |
| Microsoft Entra Agent ID | Registry moving into Agent 365 | Entra tokens | Conditional Access at sign-in | Sponsors and access packages |
| Aembit | Sees agents routed through it | Just-in-time per request | MCP Identity Gateway | Policies and audit logs |
| Token Security | Agents and MCP servers | Right-sized by intent | Flags out-of-intent actions | Owners and decommissioning |
| Oasis Security | Agents across IaaS and SaaS | Time-bound access | Policy enforcement | Lifecycle and rotation |
| SailPoint Entro | Agents, MCP servers, secrets | Just-in-time access | Behavior detection | Owners and lineage |
| Idira Secure AI Agents | Bedrock, AgentCore, Copilot Studio | Zero standing privilege | Identity Broker proxy | Lifecycle and audit |
| Clutch Security | Sanctioned and unsanctioned agents | Task-scoped credentials | Behavior alerts | Workforce Attribution |
Verdict: Aembit and Idira are the only two that sit directly between agents and MCP servers today. Token Security, Entro, and Clutch lead on finding what nobody registered. Okta and Entra win on reviews and lifecycle because they extend workflows your identity team already runs.
What Non-Human Identity Tools Cost
Most NHI tools for AI agents are sold through quotes, and only Aembit and Microsoft publish a per-unit price for agent features. Here is what each of the eight discloses, from vendor pricing pages and announcements checked on October 21, 2026.
| Tool | Pricing unit | Published price |
|---|---|---|
| Okta for AI Agents | Separate subscription | None; Agent SSO included in core Okta SSO |
| Microsoft Entra Agent ID | Per licensed user | Agent 365 $15 a month; Microsoft 365 E7 $99 a month |
| Aembit | Per agent or workload | Free for 3 agents; $20 per agent a month |
| Token Security | Quote | None |
| Oasis Security | Quote | None |
| SailPoint Entro | Quote | None |
| Idira Secure AI Agents | Add-on license | None |
| Clutch Security | Quote | None |
Verdict: Aembit is the cheapest way to pilot runtime agent access, because its free tier needs no sales call. Microsoft is easiest to budget for Microsoft tenants. For the rest, ask for a written range per identity or per agent before you run a proof of concept.
Non-Human Identity Tools We Left Off, and Why
- Astrix Security: a pioneer of NHI discovery, but Astrix ended standalone sales of new licenses on June 30, 2026, after joining Cisco.
- Permiso Security: its identity threat detection is now part of Okta after the August 26, 2026 close.
- EmpowerID: Omada acquired it on September 24, 2026, and its agent governance is moving into Omada’s platform.
- Secrets managers such as HashiCorp Vault: they store and issue secrets but do not discover agents or assign owners, so they sit under these tools.
- MCP gateways: they control tool calls more than identities, and we cover them in our MCP gateways guide.
Which Non-Human Identity Tool Should You Choose?
The right tool depends on which identity provider you run, where your agents execute, and whether you need to find agents or control them. Find the profile below that matches your team, then shortlist two tools that cover different layers before you run a proof of concept.
Teams standardized on one identity provider
- Choose Okta for AI Agents if your workforce signs in through Okta.
- Choose Microsoft Entra Agent ID if your agents run in Microsoft 365, Copilot Studio, or Azure.
- Add a discovery tool if developers run agents on laptops with personal keys.
Platform teams running agents against MCP servers
- Choose Aembit for a free pilot of brokered, secretless access.
- Choose Idira Secure AI Agents if CyberArk already guards your privileged accounts.
- Compare gateways in our Kong vs AWS AgentCore vs Docker comparison if you also need traffic policy.
Security teams starting with discovery
- Choose Token Security or Clutch Security for an independent inventory of agents and keys.
- Choose SailPoint Entro if you run SailPoint or need secrets traced to owners.
- Choose Oasis Security if you also buy Cyera for data security.
Teams responding to agent incidents
- Map response steps with the NIST, NSA, and CISA practices and trace agent actions with our AI agent observability tools roundup.
- Review MCP risks in the ToFu MCP tool bug study and the FastMCP client RCE advisories.
- Confirm every tool you shortlist can deactivate a single agent without locking out its owner.
Frequently Asked Questions
What is a non-human identity tool?
A non-human identity tool finds the credentials that software uses, such as API keys, service accounts, OAuth tokens, and AI agent identities, then assigns owners, cuts excess access, and watches usage. Tools like Okta for AI Agents, Aembit, and Token Security now treat AI agents as a distinct identity type.
Do AI agents need their own identities?
Yes. An agent that borrows an employee’s credentials shows up in logs as that employee, so you cannot audit or revoke it separately. A distinct agent identity lets security teams apply policy to the agent, review its access, and shut it off without locking out the person who deployed it.
Is Microsoft Entra Agent ID free?
Microsoft Entra Agent ID itself is available to all Microsoft Entra customers, as of October 2026. Extending Entra security features such as Conditional Access to agents requires Microsoft Agent 365 at $15 per user a month paid yearly, or Microsoft 365 E7 at $99 per user a month.
Can I still buy Astrix Security?
Not as a standalone product. Astrix ended standalone sales of new licenses on June 30, 2026, after Cisco completed its acquisition on June 29. Existing customers keep the service and support in their current agreements, and new buyers should ask Cisco when Astrix capabilities reach its identity products.
Which non-human identity tool has a free tier?
Aembit is the only tool in this guide with a free tier, as of October 2026. It covers 3 AI agents, one MCP Identity Gateway, and 5 authorization policies with 24 hours of log retention. The paid Teams plan costs $20 per agent a month and scales from 10 to 500 agents.
Related Guides
Non-human identities are one blind spot; employee sign-ups to unapproved AI apps are another. Our shadow AI detection tools guide compares 8 tools that find them.
For a head-to-head on three of the vendors in this list, see our Astrix vs Oasis vs Aembit comparison, which covers AI agent identity after the Cisco and Cyera deals.
For related coverage, see our AI agent governance platforms, AI agent security tools and AI guardrails tools.
Read the agent security hub, AI governance and security coverage, governance and compliance coverage, MCP security tools, MCP gateways, MintMCP vs Runlayer vs Lasso, Kong vs AWS AgentCore vs Docker, MCP explained, agent integration platforms, Microsoft Dynamic Agent Risk and Guardian Agents, NIST, NSA, and CISA agent incident practices, ToFu MCP tool security bugs, FastMCP client RCE advisories, and AI agent observability tools. Notes on how we work sit on editorial standards, disclosure, and contact.
The Bottom Line
Extend the identity provider you already run to cover agents, add Aembit or Idira where agents call MCP servers and APIs, and use a discovery tool to find the agents and keys nobody registered. Okta and Entra cover most lifecycle needs, while Token Security, Entro, Oasis, and Clutch fill the discovery gap.
Before you sign, confirm who will own the product in a year, ask for documentation access, and get a written price. Send corrections or tool suggestions through our contact page.